
EVPN with SR-MPLS Core
After a long journey, we finally we got to the final scenario in my ITNOG10 Segment Routing workshop: EVPN services over an SR-MPLS core.
I used the same lab topology as in the previous services-focused scenarios blog post, replacing two PE-to-host subnets with a stretched VLAN.
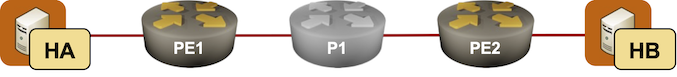
EVPN over SR-MPLS core
Does It Work?
Fortunately (for my demo) Arista implemented EVPN-over-MPLS in EOS, so I didn’t have to go shopping for another device. After the BGP session is established between the PE routers and the EVPN address family is negotiated, we can admire the EVPN type-3 routes with MPLS labels:
pe1#show bgp evpn detailBGP routing table information for VRF defaultRouter identifier 10.0.0.2, local AS number 65000BGP routing table entry for imet 10.0.0.2, Route Distinguisher: 10.0.0.2:1000Paths: 1 availableLocal- from - (0.0.0.0)Origin IGP, metric -, localpref -, weight 0, tag 0, valid, local, bestExtended Community: Route-Target-AS:65000:1000 TunnelEncap:tunnelTypeMplsMPLS label: 1040999PMSI Tunnel: Ingress Replication, MPLS Label: 16655984, Leaf Information Required: false, Tunnel ID: 10.0.0.2BGP routing table entry for imet 10.0.0.3, Route Distinguisher: 10.0.0.3:1000Paths: 1 availableLocal10.0.0.3 from 10.0.0.3 (10.0.0.3)Origin IGP, metric -, localpref 100, weight 0, tag 0, valid, internal, bestExtended Community: Route-Target-AS:65000:1000 TunnelEncap:tunnelTypeMplsMPLS label: 1040999PMSI Tunnel: Ingress Replication, MPLS Label: 16655984, Leaf Information Required: false, Tunnel ID: 10.0.0.3
Unfortunately, we can’t see the two-label stack in the EVPN routes on Arista EOS. We have to use another command to figure out how the local device (PE1) reaches the remote PE router (PE2), and we have to go even further if we want to see the actual label:
pe1#show tunnel rib 10.0.0.3/32 candidatesTunnel RIB: system-tunnel-ribEndpoint Tunnel Type Index(es) Tunnel Preference Tunnel Metric----------------- ------------------- --------------- ----------------------- -------------10.0.0.3/32 IS-IS SR IPv4 2 65 0
However, once HA pings HB, we get the EVPN type-2 routes:
pe1#show bgp evpn route-type mac-ip detailBGP routing table information for VRF defaultRouter identifier 10.0.0.2, local AS number 65000BGP routing table entry for mac-ip aac1.ab6b.03b4, Route Distinguisher: 10.0.0.2:1000Paths: 1 availableLocal- from - (0.0.0.0)Origin IGP, metric -, localpref -, weight 0, tag 0, valid, local, bestExtended Community: Route-Target-AS:65000:1000 TunnelEncap:tunnelTypeMplsMPLS label: 1047390 ESI: 0000:0000:0000:0000:0000BGP routing table entry for mac-ip aac1.abb4.bb24, Route Distinguisher: 10.0.0.3:1000Paths: 1 availableLocal10.0.0.3 from 10.0.0.3 (10.0.0.3)Origin IGP, metric -, localpref 100, weight 0, tag 0, valid, internal, bestExtended Community: Route-Target-AS:65000:1000 TunnelEncap:tunnelTypeMplsMPLS label: 1047390 ESI: 0000:0000:0000:0000:0000
And finally, we can look at the layer-2 routing table (L2RIB) to observe the MPLS label stack (even though the transport label is still not displayed):
pe1#show l2rib input all detailcaf0.0001.0001, VLAN 1006, seq 1, pref 16, learnedDynamicMac, source: Local DynamicEthernet1aac1.ab6b.03b4, VLAN 1000, seq 1, pref 16, learnedDynamicMac, source: Local DynamicEthernet2aac1.ab82.bb99, VLAN 1006, seq 1, pref 16, learnedDynamicMac, source: Local DynamicEthernet1aac1.abb4.bb24, VLAN 1000, seq 1, pref 16, evpnDynamicRemoteMac, source: BGPLabel entry 1: 1047390Tunnel IS-IS SR IPv4 (2), TEP 10.0.0.3/32
Lab Topology
Here are the changes I made to the MPLS/VPN topology to replace MPLS/VPN with EVPN services:
- I removed MPLS- and VRF-related settings
- I had to configure SR-MPLS transport for EVPN (the default transport is VXLAN):
evpn.transport: sr
- The edge devices (PE routers) use VLAN and EVPN modules instead of MPLS and VRF:
groups:edge:members: [ pe1, pe2 ]module: [ isis, bgp, sr, vlan, evpn ]
- The PE-to-host links are defined as part of the tenant VLAN:
vlans:tenant:mode: bridgelinks: [ ha-pe1, hb-pe2 ]
- Finally, I had to enable EVPN for the tenant VLAN (that’s done automatically for VXLAN-enabled VLANs, but we cannot use the same trick for MPLS-based EVPN):
evpn.vlans: [ tenant ]
The final lab topology is here.
Try It Out
The workshop GitHub repository includes the installation guidelines; you might want to read them first. After that, you can:
- Start a GitHub Codespace
- Import an Arista cEOS container into it (alternate step-by-step instructions)
- Change directory to
2-fun/3-evpn - Execute netlab up
- Have fun